Answer every security question with confidence.
SecuDraft turns approved policies and evidence into review-ready answers—so enterprise teams move faster without surrendering control.
Do you enforce MFA for all production access?
Yes — enforced via Okta; FIDO2 keys for privileged roles.
↳ Access Control Policy §4.1
Is customer data encrypted at rest?
AES-256 using AWS KMS customer-managed keys, rotated annually.
↳ Encryption Standard v1.4
Do you support customer-managed keys (BYOK)?
No approved source found. Left for human review.
↳ —
85%
of answers drafted on first pass
From your approved library and evidence—before a human touches the file.
3 days → 3 hours
typical turnaround
Intake to review-ready export, with citations attached to every answer.
100%
of answers cited
Every draft links back to the exact policy, certification, or past answer.
0
invented answers
Unsupported questions are flagged Missing Evidence, never guessed.
The operational gap
Security review should not be the slowest system in the enterprise.
Questionnaires arrive in inconsistent formats, approved knowledge is scattered across documents, and every unsupported answer creates risk. SecuDraft brings the workflow into one governed operating layer.
How it works
One controlled path from intake to delivery.
Upload
Drop in XLSX, CSV, DOCX, or PDF. Any layout, any length.
Extract
Every question is detected, sectioned, and mapped to its answer cell.
Match & draft
Answers are drafted only from your approved library, policies, and evidence.
Review
Confidence scores and citations on every answer. Uncertain ones are flagged.
Export
Write answers back into the original file format, ready to send.
Control plane
Built for the people accountable for every answer.
Citations on every answer
See the exact policy clause, certification, or past answer behind each draft.
Honest confidence labels
Approved, Needs Review, Missing Evidence, or Draft. Never a guess dressed as fact.
Approved answer library
Every approval strengthens your source of truth for the next questionnaire.
Evidence vault
SOC 2, ISO, pen tests, and policies with expiry tracking and NDA gating.
Team review
Assign sections, comment inline, and track status across sales and security.
Full audit trail
Every edit, approval, and export is logged for compliance.
Compounding knowledge
Every questionnaire makes the next one faster.
Approvals, policies, and evidence flow into a single governed library. The next questionnaire starts from everything your organization has already verified—so answers get sharper with every deal.
- Approved answers are reused automatically across new questionnaires
- Expiring certifications and policies surface before they go stale
- Sales, security, and legal work from the same verified source
Security architecture
Trust is designed into the workflow, not added after it.
The same rigor your customers expect from your answers governs how SecuDraft handles access, evidence, and approvals.
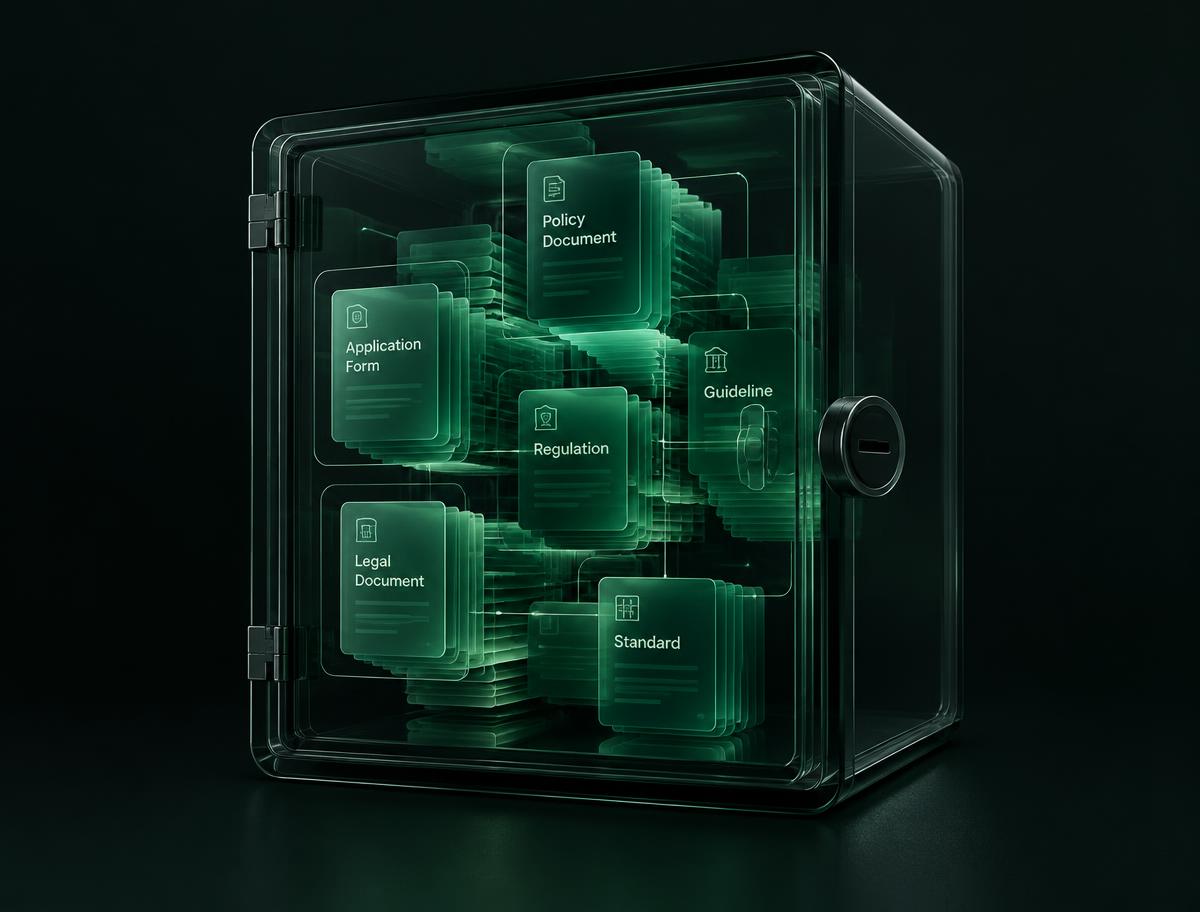
- Strict organization-level data isolation
- Encryption in transit (TLS 1.2+) and at rest (AES-256)
- Your data is never used to train models
- SSO, role-based access, and full audit logs
- AI processing runs server-side only
Connected operations
Works across your existing technology estate.
"The fastest answer is worthless if it can't be defended. The defensible answer is the one that wins the deal."
The principle behind every SecuDraft workflow
Plans
A plan for every stage of security operations.
Starter
For teams establishing a repeatable review process
- Questionnaire automation
- 3 seats
- Answer library
- XLSX & CSV export
Growth
PopularFor scaling sales and security organizations
- Higher processing volume
- 15 seats
- Evidence vault
- All export formats
- Comments & assignments
Enterprise
For complex and regulated organizations
- Custom processing volume
- SSO / SCIM
- AI assistant API
- Dedicated region
- Custom DPA
SecuDraft for ChatGPT
Your security profile, inside ChatGPT.
Connect SecuDraft once and your team can ask ChatGPT anything about your security posture. It answers straight from your approved library, cites the source, and says so when there is no approved answer yet.
Approved answers only
The connector reads your approved library and evidence — never the open web, never a guess.
Scoped per user
Each assistant request runs as the signed-in member, with their role and NDA restrictions applied.
Cited and logged
Every response carries its source, and the full request lands in your audit trail.
Read-only by default
Assistants can query your security profile but can't edit answers, approvals, or documents.
ChatGPT·SecuDraft connectorDo we support SSO and SCIM provisioning for enterprise customers?
Yes. SecuDraft supports SSO via SAML 2.0 and OIDC through Okta, Azure AD, and Google Workspace, with SCIM 2.0 for automated provisioning and deprovisioning. Access is role-based, and privileged roles additionally require FIDO2 keys.
3 approved sources · confidence 96%
Can we offer customer-managed keys (BYOK)?
I couldn't find an approved source for BYOK support, so I won't guess. Nothing in your answer library, policies, or certifications covers it. I've flagged this for your security team and logged the request.
no approved source · routed for human review
Questions, answered.
Make security review an enterprise advantage.
Bring your next questionnaire into a controlled, evidence-backed workflow.
Start a questionnaire